Introduction
Artificial Intelligence (AI) is rapidly transforming the way businesses operate, make decisions and deliver services. From automating routine business processes and improving customer experiences to analysing complex data and supporting strategic decisions, AI has become an important driver of digital transformation.
However, as organizations increasingly adopt AI technologies, they also face new challenges related to data privacy, cybersecurity, regulatory compliance, ethical considerations and operational risks.
This is where AI Governance becomes essential.
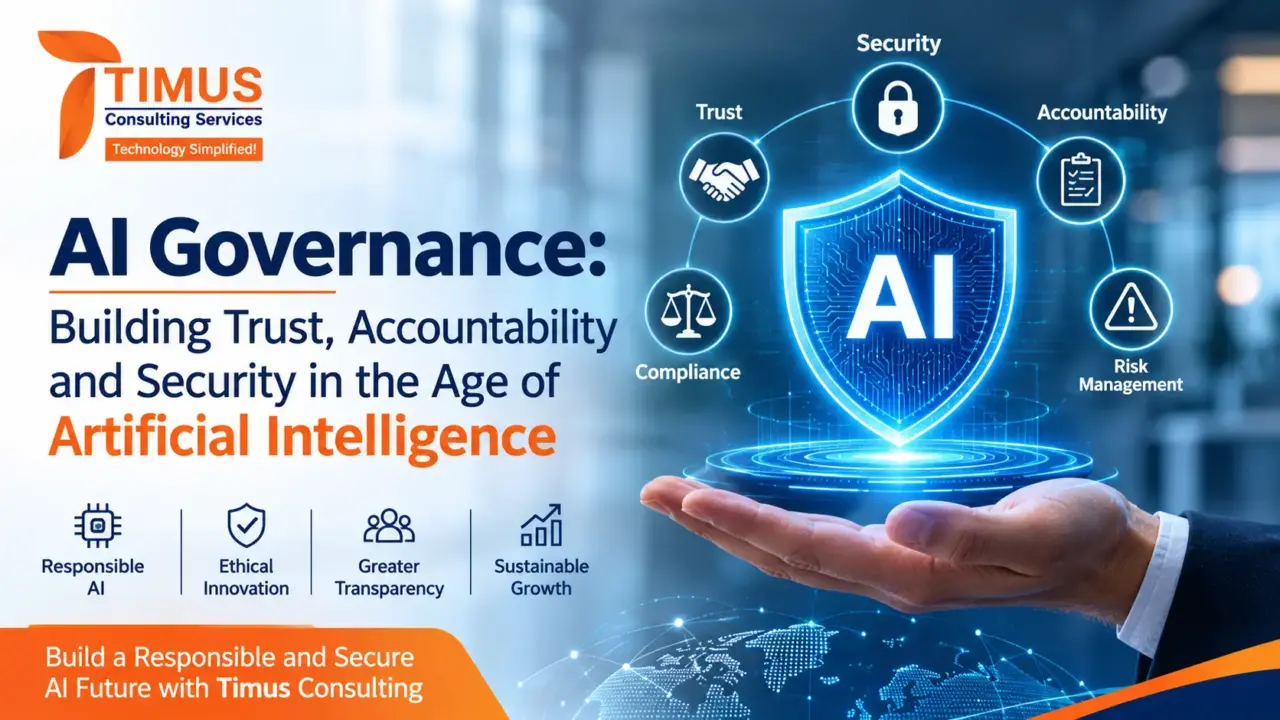
AI Governance provides a structured approach to managing how AI technologies are developed, implemented, monitored and used within an organization. It ensures that AI systems operate responsibly, transparently, securely and in alignment with business objectives, regulatory requirements and ethical principles.
The goal is not to restrict innovation but to enable organizations to adopt AI confidently while maintaining control over the associated risks.
What Is AI Governance?
AI Governance refers to the policies, processes, frameworks, roles and controls established to ensure the responsible development, deployment and use of Artificial Intelligence.
It defines how organizations manage AI-related risks, establish accountability, protect sensitive information and ensure that AI-driven decisions remain transparent, fair and reliable.
An effective AI Governance framework addresses the entire AI lifecycle, including:
- AI strategy and planning.
- Data collection, processing and management.
- AI model development and testing.
- Deployment and integration.
- Performance monitoring and evaluation.
- Risk assessment and mitigation.
- Ongoing compliance and improvement.
Why Is AI Governance Important?
As AI becomes embedded in critical business operations, organizations cannot rely solely on technology teams to manage its risks. A comprehensive governance structure is necessary to ensure that AI systems deliver value without introducing unacceptable business, legal or operational exposure.
Some of the key reasons AI Governance is important include:
1. Managing AI-Related Risks
AI systems can produce inaccurate outputs, make biased recommendations or behave unpredictably when exposed to unfamiliar data. Without appropriate oversight, these issues can affect business decisions and organizational reputation.
AI Governance helps organizations identify, assess, prioritize and mitigate risks throughout the AI lifecycle.
2. Data Privacy and Protection
AI systems often process large volumes of organizational, customer and employee information. Improper data handling can result in privacy violations, unauthorized access and information leakage.
Strong governance practices establish guidelines for data classification, access management, encryption, retention and secure data usage.
3. Regulatory Compliance
Governments and regulatory authorities worldwide are introducing requirements and guidance to address AI-related risks.
Organizations operating across different regions must understand the regulatory obligations applicable to their AI systems, business activities and industry.
AI Governance helps establish the policies, documentation and controls required to demonstrate responsible practices and support regulatory compliance.
4. Transparency and Accountability
Businesses must understand how AI systems generate outputs and influence decisions, particularly in sensitive areas such as financial services, recruitment, healthcare and customer management.
Governance ensures that responsibilities are clearly assigned, decisions can be reviewed and appropriate human oversight is maintained.
5. Building Customer and Stakeholder Trust
Customers, employees, business partners and regulators expect organizations to use AI responsibly.
Transparent AI practices, effective security controls and clear accountability help build confidence in AI-powered products and services.
Key Pillars of an Effective AI Governance Framework
An effective AI Governance framework should address the following essential areas:
1. AI Policies and Organizational Accountability
Organizations should establish a formal policy defining acceptable AI usage, business responsibilities, approval processes and accountability structures.
A dedicated AI Governance Committee or cross-functional working group can oversee AI initiatives and ensure that AI adoption aligns with organizational objectives.
2. AI Risk Management
AI-related risks must be identified and assessed before systems are introduced into business operations.
Risk assessments should consider:
- Model accuracy and reliability.
- Algorithmic bias and discrimination.
- Data privacy and confidentiality.
- Cybersecurity vulnerabilities.
- Third-party and vendor risks.
- Regulatory and legal exposure.
- Business continuity and operational impact.
Risk assessments should also be repeated whenever significant changes are made to AI models, data sources or business use cases.
3. Data Governance and Security
Data is the foundation of most AI systems. Organizations must establish controls to ensure that the information used by AI systems is accurate, relevant, secure and appropriately authorized.
Important controls include data classification, access restrictions, encryption, data quality management, retention policies and data lineage.
4. Ethical and Responsible AI
AI systems should be designed and used in ways that respect human rights, fairness, privacy and organizational values.
Organizations should implement measures to identify and reduce bias, prevent discriminatory outcomes and ensure that AI systems are used for legitimate business purposes.
5. Human Oversight
AI should support human decision-making rather than automatically replace accountability.
Organizations should define when human review or approval is required, particularly for high-impact decisions involving employees, customers, financial transactions or regulatory matters.
6. Continuous Monitoring and Auditing
It is not a one-time exercise. AI models and their operating environments evolve over time, which can affect accuracy, security and reliability.
Regular monitoring, internal audits, performance assessments and incident reviews help organizations identify emerging risks and maintain effective controls.
Major AI Governance Frameworks and Standards
Organizations can refer to established international frameworks and standards to develop a structured program.
1. ISO/IEC 42001 – Artificial Intelligence Management System
ISO/IEC 42001:2023 provides requirements for establishing, implementing, maintaining and continually improving an Artificial Intelligence Management System (AIMS).
It helps organizations establish formal governance processes, manage AI-related risks, define responsibilities and demonstrate their commitment to responsible AI practices.
2. NIST AI Risk Management Framework (AI RMF)
Developed by the National Institute of Standards and Technology (NIST), the AI RMF provides a voluntary approach to managing AI-related risks and promoting trustworthy AI systems.
It is structured around four key functions:
- Govern – Establish organizational policies, responsibilities and oversight.
- Map – Understand AI use cases, context and potential risks.
- Measure – Evaluate and assess AI risks and system performance.
- Manage – Prioritize and address identified risks.
3. EU Artificial Intelligence Act
The EU AI Act establishes a regulatory framework for AI systems based on their associated risk levels.
It introduces different requirements for prohibited AI practices, high-risk AI systems, transparency obligations and general-purpose AI models.
Organizations that develop, provide, deploy or use AI systems within the scope of the legislation must understand their respective responsibilities and applicable obligations.
Common AI Governance Challenges
Despite the growing importance, many organizations face practical challenges when implementing it.
Some of the most common challenges include:
- Lack of a clearly defined AI strategy and governance structure.
- Limited awareness of AI-related risks among employees and leadership.
- Uncontrolled use of publicly available AI tools.
- Insufficient data privacy and security controls.
- Difficulty identifying and monitoring AI systems across departments.
- Limited transparency into third-party AI models and services.
- Challenges in keeping pace with evolving regulatory requirements.
- Lack of skilled professionals with AI risk and governance expertise.
How Organizations Can Implement AI Governance
Organizations do not need to transform their entire technology environment overnight. They can adopt a phased approach to establish effective AI Governance.
Step 1: Identify AI Usage Across the Organization
Create an inventory of AI systems, tools, applications and services currently being used or planned across different departments.
Step 2: Establish AI Governance Policies
Develop an AI usage policy covering acceptable use, data protection, accountability, approval requirements and employee responsibilities.
Step 3: Conduct AI Risk Assessments
Evaluate AI systems based on their business purpose, data sensitivity, potential impact, security exposure and regulatory obligations.
Step 4: Implement Security and Compliance Controls
Establish appropriate technical and organizational controls, including access management, encryption, monitoring, human oversight and documentation.
Step 5: Define Roles and Responsibilities
Assign clear ownership for AI systems, risk assessments, compliance monitoring, incident management and periodic reviews.
Step 6: Train Employees and Stakeholders
Conduct awareness sessions to educate employees about responsible AI usage, data confidentiality, potential risks and organizational policies.
Step 7: Monitor, Audit and Improve
Regularly assess AI systems, review governance effectiveness, track incidents and update policies to address emerging risks and technological changes.
The Future of AI Governance
As organizations increasingly adopt Generative AI, Large Language Models (LLMs), AI-powered automation and autonomous AI agents, governance requirements will become more complex.
Future AI Governance practices will need to address emerging concerns such as AI-generated misinformation, prompt injection, model manipulation, unauthorized data exposure, autonomous decision-making and third-party AI dependencies.
Organizations will also need to move beyond traditional IT governance approaches and establish AI-specific risk management and assurance capabilities.
Conclusion
Artificial Intelligence offers significant opportunities for organizations to improve efficiency, accelerate innovation and strengthen business decision-making. However, these benefits can only be sustained when AI technologies are implemented with appropriate governance, security and accountability.
AI Governance is no longer simply a technology consideration. It is a business priority that requires leadership commitment, cross-functional collaboration and continuous risk management.
By adopting recognized frameworks such as ISO/IEC 42001 and the NIST AI Risk Management Framework, organizations can establish a strong foundation for responsible AI adoption.
The future belongs to organizations that do not just adopt AI, but govern it responsibly.
Frequently Asked Questions
1. What is AI Governance?
AI Governance is a framework of policies, processes, and controls that ensures AI systems are developed and used responsibly, securely, and transparently.
2. Why is AI Governance important for businesses?
It helps businesses manage AI risks, ensure regulatory compliance, protect sensitive data, and build trust among customers and stakeholders.
3. What are the key pillars of AI Governance?
The key pillars include transparency, accountability, data privacy, security, fairness, risk management, and regulatory compliance.
4. How does AI Governance help manage AI risks?
It helps identify potential risks such as data bias, security vulnerabilities, inaccurate outputs, and privacy breaches through continuous monitoring and risk assessments.
5. What is the role of GRC in AI Governance?
Governance, Risk, and Compliance (GRC) helps organizations establish AI policies, monitor risks, maintain accountability, and align AI practices with regulatory requirements.