Introduction
Artificial Intelligence (AI) is transforming the way we live and work. From personalized recommendations and virtual assistants to healthcare systems and financial services, AI is becoming an integral part of our daily lives. However, as AI systems become more powerful, an important question arises: How can we innovate with AI while protecting people’s privacy?
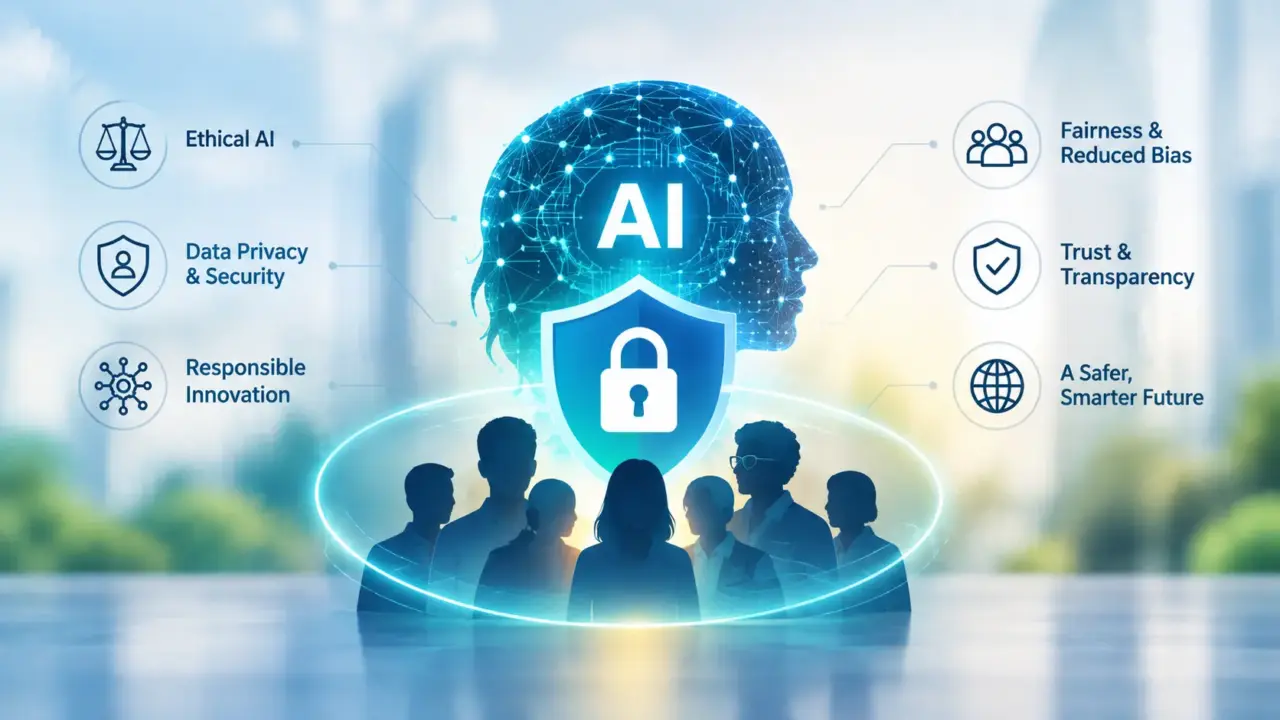
Responsible AI is not just about building intelligent systems. It is about ensuring that these systems operate ethically, securely, and transparently while respecting individual rights. Data privacy is one of the most important pillars of this responsibility.
Why Data Privacy Matters in AI
AI systems rely on data to learn, identify patterns, and generate predictions. This data may include personal information, financial records, health details, customer preferences, and business information.
When such data is collected or processed without adequate safeguards, it can expose individuals and organizations to privacy risks.
For example, an AI-powered customer service tool might process customer conversations to provide faster responses. If sensitive information is stored unnecessarily or exposed to unauthorized users, it can create serious privacy concerns.
Protecting data is therefore essential not only for regulatory compliance but also for maintaining trust.
Key Privacy Challenges in AI
1. Excessive Data Collection
AI systems may collect more information than necessary to perform a task. Gathering excessive personal data increases the risk of misuse, unauthorized access, and accidental exposure.
2. Lack of Transparency
People may not always know how their information is being collected, used, or shared by AI-powered applications. Without clear explanations, it becomes difficult to make informed decisions about sharing personal data.
3. Data Security Risks
AI systems can become targets for cyberattacks, data breaches, and unauthorized access. Weak security controls can expose sensitive information and undermine confidence in AI technologies.
4. Misuse of Personal Information
Personal data collected for one purpose may be used for another without adequate justification or appropriate safeguards. Responsible AI requires organizations to establish clear boundaries around how data can be used.
5. Risks Associated with Generative AI
Generative AI tools can sometimes reproduce sensitive information contained in their training data or process confidential information entered by users. Organizations must therefore establish clear guidelines for using these tools safely.
Principles of Responsible AI and Data Privacy
Organizations can address these challenges by adopting a privacy-focused approach to AI development and implementation.
Data minimization: Collect only the information necessary for a specific purpose.
Transparency: Clearly communicate how personal data is collected, processed, and used.
Security by design: Integrate appropriate security measures throughout the AI system’s lifecycle.
Accountability: Assign responsibility for monitoring AI systems and addressing privacy risks.
Human oversight: Ensure that appropriate people can review important decisions and intervene when necessary.
Privacy by design: Build privacy protections into AI systems from the beginning rather than adding them after deployment.
How Organizations Can Use AI Responsibly
Responsible AI requires more than policies. It requires practical action.
Organizations should conduct privacy and risk assessments before deploying AI applications, establish clear data-handling procedures, restrict access to sensitive information, and regularly evaluate their systems for security vulnerabilities.
Employees should also receive guidance on using AI tools responsibly. For instance, they should avoid entering confidential customer information, passwords, financial records, or proprietary business data into AI tools that have not been approved for such use.
Where appropriate, organizations can use techniques such as data anonymization, pseudonymization, and controlled access to reduce exposure of personal information. These techniques should be evaluated carefully because they do not eliminate every privacy risk.
Organizations must also comply with applicable data protection laws and review their practices as regulations and AI technologies evolve.
Building Trust Through Responsible AI
Trust is essential for the long-term success of AI. Customers, employees, and other stakeholders need confidence that their information will be handled carefully and that AI systems will not compromise their rights.
Organizations that prioritize privacy, transparency, and accountability can strengthen relationships with stakeholders while reducing avoidable risks.
Responsible AI should not be viewed as a barrier to innovation. Instead, it provides a foundation for developing technologies that are useful, reliable, and respectful of people.
Conclusion
Artificial Intelligence offers enormous opportunities to improve efficiency, support decision-making, and solve complex problems. However, technological progress must go hand in hand with the protection of personal information.
Responsible AI and data privacy are shared responsibilities that involve developers, organizations, regulators, and users. By embedding privacy into AI systems, establishing strong governance practices, and promoting awareness, we can create a digital future in which innovation and individual rights coexist.
The future of AI should not be measured only by what technology can achieve, but also by how responsibly it protects the people it serves.
FAQs: Responsible AI and Data Privacy
1. What is responsible AI?
Responsible AI refers to designing and using artificial intelligence systems ethically, transparently, and fairly while minimizing risks such as bias, discrimination, and misuse of personal data.
2. Why is data privacy important in AI?
Data privacy protects sensitive personal information from unauthorized access, misuse, and exposure. It helps organizations build trust and comply with applicable data protection regulations.
3. How can organizations protect personal data when using AI?
Organizations can protect personal data by implementing encryption, access controls, data minimization, anonymization, regular security audits, and clear data governance policies.
4. What are the main risks of AI and data privacy?
Key risks include unauthorized data collection, data breaches, algorithmic bias, identity exposure, lack of transparency, and the misuse of personal information by AI systems.
5. How does AI governance support responsible AI?
AI governance establishes policies, accountability, risk management processes, and monitoring practices to ensure AI systems operate safely, fairly, transparently, and in compliance with relevant regulations.
6. What regulations protect data privacy in AI applications?
Relevant regulations include the General Data Protection Regulation (GDPR) in the European Union and India’s Digital Personal Data Protection Act, 2023, alongside applicable rules and sector-specific requirements.